Understanding CORS
S
I am an engineering student who loves learning new stuff.
Simply CORS is fetching resources from other application having different origin than the client-side.
Applying a CORS restriction is a security feature defined by a server and implemented by a browser.
How to know we are making a cross-origin-request?
First, we have to know what origin comprises of.
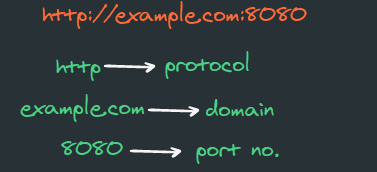 So when we make a request to an origin which differs in any of the above mentioned parameters then it is CORS.
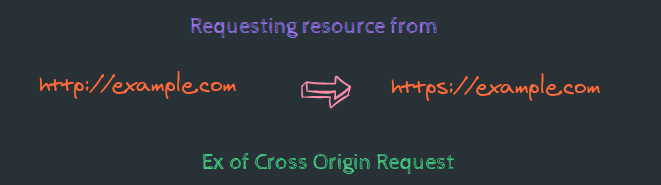
So how it works:
- So when any application having endpoint https://example.com makes a request to a https://example-server.com browser embeds
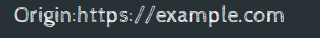 in the request.
- When the server receives a request & if it wants to share its resources then
it will add

- Server also adds another field response.type of cors or opaque.
- If a request is made for a resource on another origin which returns the CORs headers, then the type is cors.
- Opaque response is for a request made for a resource on a different origin that doesn't return CORS headers.
- When the browser receives a response if it finds the relevant Access-Control-Allow-Origin header, the browser allows the response data to be shared with the client site.
Thanks for reading this article.